

CME to Enhance Security of OAuth Authenticated Services
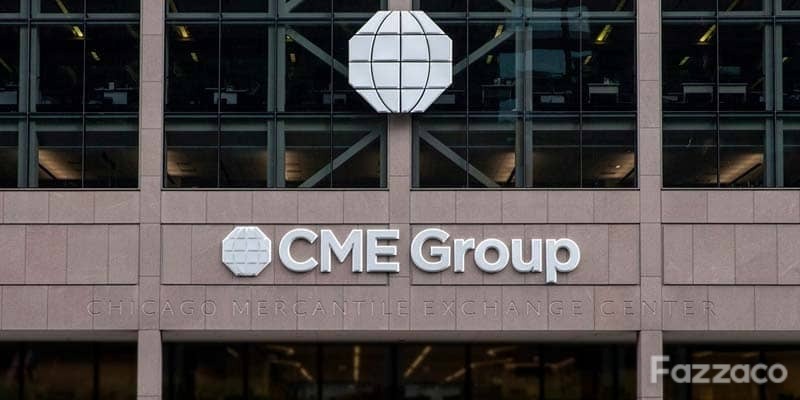
CME Group recently announced that the access to OAuth authenticated services will require a case-sensitive API ID on all requests, effective Saturday, October 30, in order to provide the highest levels of market integrity, including the security of CME Group and adjacent ecosystems.
Currently, the following services use OAuth authentication:
Reference Data API
CME GC Allocator API
The exchange noted in its announcement that relevant companies need to verify all applications, scripts and services are using the API ID case (uppercase and/or lowercase) registered with CME Group to avoid any service interruptions.
OAuth is an open protocol that allows secure authorization in a simple and standard method from web, mobile and desktop applications. It specifies a process for resource owners to authorize third-party access to their server resources without sharing their credentials.
The protocol is designed specifically to work with Hypertext Transfer Protocol (HTTP). It allows access tokens to be issued to third-party clients by an authorization server, with the approval of the resource owner. The third party then uses the access token to access the protected resources hosted by the resource server.
 Subscribe Now