

Shufti: Broker KYC, AML Monitoring and Withdrawal Verification
Shufti brings identity verification, anti-money laundering screening and fraud signals into a platform that spans customer onboarding and subsequent account activity. For forex and CFD brokers, its relevance extends from checking an applicant’s documents to recognising linked registrations, reviewing changes in customer risk and authenticating sensitive actions such as withdrawals. The operational question is how these checks connect to the broker’s client records and decision-making responsibilities.
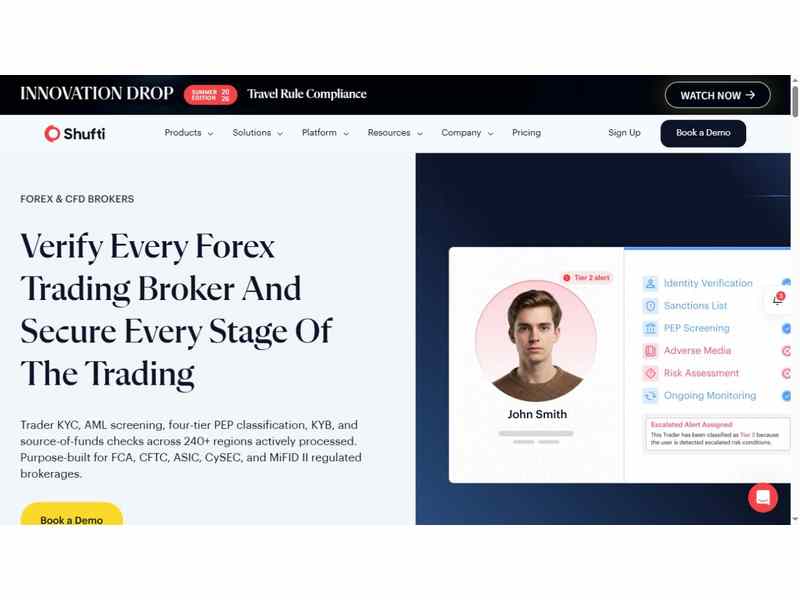
Shufti’s forex and CFD broker product page. Image: Shufti.
From an onboarding check to an ongoing customer record
Shufti organises its platform around three stages: Onboard, Monitor and Assure. Onboard covers identity and customer or business due diligence. Monitor adds continuing screening, transaction monitoring and fraud analysis. Assure applies verification to higher-risk actions after an account has been opened. This structure addresses a familiar gap in brokerage operations: an identity accepted at registration does not establish that every later login, payment instruction or bank-account change is legitimate.
The company’s forex offering, presented as Trader Trust OS, describes a customer lifecycle running from registration and identity verification through assessment, funding, trading, withdrawals, account maintenance and periodic review. These are proposed points for checks within a broker’s workflow, rather than evidence that the provider executes trades, operates the brokerage ledger or determines a firm’s regulatory obligations. The broker still needs to define which events require a decision and which system owns the resulting account state.
Identity verification with several evidence paths
The identity stack includes document verification, face verification, electronic identity verification, NFC verification and live-agent VideoIdent. Document checks combine information extraction with document analysis; face verification links the person completing the journey to the identity being presented and adds liveness checks. Electronic verification uses external data sources, while NFC reads information held on supported identity-document chips. Each route supplies a different form of evidence and can create a different customer experience.
That distinction matters when a broker serves customers with different documents, devices and levels of digital familiarity. A camera-based journey may work well for one segment but need a fallback for another. Product availability on a platform does not mean every document, country or handset supports every route. A practical rollout therefore starts with the actual applicant mix and defines what happens when a document is unreadable, a chip cannot be read or a customer cannot complete the selected process.
Shufti also offers reusable identity through Fast ID and additional address-verification options. Reuse can reduce repeated customer input, but the accepting broker must establish what evidence is transferred, how recently it was obtained and whether new checks are needed. Address evidence likewise needs a defined role: a declared address, a verified document and a device-location signal are related inputs, not interchangeable proof of the same fact.
Risk-based journeys and analyst decisions
Shufti describes configurable risk tiers, due-diligence forms and customer-risk assessment as parts of its onboarding architecture. For a brokerage, these capabilities can support different paths for straightforward applications and cases needing more information. The useful outcome is a controlled escalation process: collect the missing evidence, direct the case to the appropriate reviewer and preserve the explanation for the final disposition.
Identity verification and an investment-service assessment also answer different questions. Establishing who a customer is does not establish their experience, financial circumstances or eligibility for a particular service. Shufti’s forex materials include assessment stages, but a broker should examine the actual questionnaires, decision rules and records available in the proposed configuration. The same applies to source-of-funds checks: the workflow must specify what is requested, what the technology checks and what remains an analyst judgment.
For corporate customers, Shufti’s KYB and beneficial-owner capabilities add company, director and ownership information to the process. These cases need a clear link between the business being onboarded and the individuals who control it or are authorised to act for it. The value lies in keeping that evidence connected to the customer file, particularly when ownership details or authorised representatives later change.
AML screening and monitoring beyond the first match
Shufti lists sanctions, politically exposed person and adverse-media screening alongside ongoing monitoring. Screening creates candidates for review; an apparent name match still needs context before it becomes a customer decision. Its AI Compliance Copilot is presented as a tool for reviewing matches and providing reasoning and confidence information to analysts. That explanation is useful only if reviewers can inspect the underlying evidence and retain their own disposition.
The company also markets transaction monitoring with configurable rules, supported by an AI-assisted rule builder and backtesting. In a brokerage environment, the data feeding those rules is as important as the rule library itself. Deposits, withdrawal requests, payment-method changes and customer attributes need consistent identifiers and timestamps. If those events arrive late or are split across payment and CRM systems, an otherwise capable monitoring product can still receive an incomplete account history.
A broker evaluating this layer should test how alerts become cases, who receives them and how a resolution returns to the operational system. It should also establish which screening changes trigger renewed review and whether an unresolved case restricts a specific action or the account more broadly. These are workflow choices to implement and validate, not outcomes that follow automatically from enabling an AML module.
Connected-account fraud and promotion abuse
The forex product page gives particular attention to synthetic identities, stolen identities, multi-accounting and referral or bonus abuse. Shufti describes combining device fingerprinting, behavioural signals, facial deduplication and a Fraud Hub to identify connections across registrations. A series of applications may look unrelated when examined one by one yet share infrastructure or identity signals that justify a closer review.
For brokers running acquisition campaigns, this is a different problem from checking whether a single ID document is genuine. The question is whether an applicant belongs to a coordinated group exploiting a promotion or whether the same person is returning under another identity. Keeping cross-account signals with the case can help an analyst understand why a registration was escalated and distinguish the suspected behaviour from an ordinary document failure.
Shared devices and networks are not conclusive evidence of abuse. Households, workplaces and shared connectivity can create legitimate overlap, so thresholds and reviewer access matter. A useful pilot includes both known abusive patterns and legitimate shared-device cases. The goal is to establish how the proposed configuration separates them and how a customer can complete additional verification when an automated signal is insufficient.
Withdrawals and account changes as separate control points
Shufti’s Assure products include bank-account verification, step-up authentication and multi-factor authentication. Its forex positioning specifically highlights checking bank-account ownership before withdrawals. These features can connect an existing verified identity to a new request, rather than treating the original onboarding result as permanent authorisation for every subsequent instruction.
A withdrawal workflow illustrates the difference. The brokerage must know who owns the destination account, whether the customer’s device or behaviour has changed and whether additional authentication is warranted. Shufti describes live-face authentication and escalation from other authentication methods. The broker then needs to decide how a passed, failed or incomplete check affects the withdrawal request and how customer service handles the exception.
Bank-account verification does not itself move the funds, and an identity check is not a payment reconciliation process. The connection to the broker’s CRM, payments workflow and account ledger therefore remains essential. A changed payout destination should not be approved in one system while another continues using an older decision. Testing should cover both successful checks and interrupted journeys, including a customer who abandons additional verification.
Integration, deployment and operational ownership
Shufti presents a REST API for its trader lifecycle capabilities and offers SaaS, private-cloud and on-premises deployment options. Its platform materials also describe regional hosting and configurable journeys. These choices give a procurement team several architectural questions to resolve: where information is processed, which components are included in the selected deployment and who maintains configuration and service updates.
The interface design should make verification status unambiguous. A broker needs to distinguish an unstarted check, a request awaiting customer input, a completed result and a case awaiting human review. Engineering teams should examine notification delivery, retries, duplicate events and the mapping between Shufti records and internal customer identifiers. A demonstration of a successful API response is only one part of proving that the surrounding workflow behaves predictably.
Data access and retention deserve equally concrete treatment because the platform can combine documents, biometric checks, device information and transaction events. Access should follow the responsibilities of compliance, fraud, customer-service and engineering teams. Procurement should obtain the applicable processing and retention terms and establish how records are retrieved, corrected or removed under the agreed arrangement. Deployment labels alone do not answer those questions.
Where Shufti fits in a brokerage stack
Shufti is most relevant where a broker wants identity evidence, continuing risk signals and authentication of sensitive actions to share customer context. Its breadth creates opportunities to connect controls that are often purchased separately, but the benefit depends on the modules selected and the quality of the integration. Firms seeking only a document check may have a narrower implementation than those connecting onboarding, monitoring and withdrawals.
A meaningful pilot follows complete customer journeys: a straightforward application, a case needing extra evidence, a possible screening match, linked registrations and a withdrawal requiring additional authentication. Measure completion and review times, exception handling and the completeness of the resulting case record using the broker’s own customer mix. That provides a stronger basis for a decision than treating a vendor-wide speed or coverage claim as a forecast for the brokerage.
 Subscribe Now